LOADING THE ENGINEERING STORY

SAIFLIX
A SAI KRISHNA ORIGINAL
CLOUD & DEVOPS ENGINEER • AZURE

I engineer cloud infrastructure into
automated. resilient.
production-ready systems.

Cloud & DevOps engineer focused on Azure, AWS, Terraform, Docker, Kubernetes, RedHatEnterprise Linux, hybrid infrastructure, and automation. Explore the systems I support, the labs I build, and the lessons I document.

OPEN TO OPPORTUNITIESHYDERABAD · BENGALURU · REMOTE
SCROLL TO EXPLORE↓
THE PERSON BEHIND THE SYSTEMS

Sai Krishna · Cloud & DevOps

Azure • Terraform • Hybrid Cloud • Infrastructure Automation

02.6+YEARS IN IT*
03AZURE CERTIFICATIONS*
∞CURIOSITY FOR AUTOMATION
Experience and credentials should always match the dates and badges on my current resume.
THE FEATURED COLLECTION

Projects worth watching.

Not just tools on a resume. Practical builds, the decisions behind them, and what I learned along the way.

INFRASTRUCTURE / 02
DRIFT DETECTED → REVIEW
AUTOMATION · GOVERNANCE

Terraform Drift Detection

Detect infrastructure changes outside code and create a repeatable review workflow with automation.

TerraformGitHub ActionsOIDC
View repository ↗
CLOUD PLATFORM / 03
AZURE
CLOUD · INFRASTRUCTURE AS CODE

Azure Infrastructure Lab

Build repeatable cloud resources and explore networking, identity, security, and infrastructure lifecycle management.

AzureTerraformNetworking
Project details ↗
DELIVERY SYSTEMS / 04
CODE
→
BUILD
→
DEPLOY
CITESTCD
DELIVERY · AUTOMATION

CI/CD Pipeline Lab

Explore pipeline stages, repeatable builds, deployment checks, and safer release practices.

Azure DevOpsGitHub ActionsYAML
Project details ↗
AZURE PLATFORM / 05
HUB VNET↔SPOKE VNETBASTION · MONITOR · LOG ANALYTICS
AZURE · TERRAFORM · CI/CD

Enterprise Azure Landing Zone

Reusable Terraform modules for networking, Azure Bastion, virtual machines, diagnostics, remote state, and approval-based GitHub Actions workflows.

AzureTerraformGitHub Actions
View repository ↗
MULTI-CLOUD / 06
AZURE↔AWS
ONE WORKFLOW · SEPARATE DEPLOYMENTS
CLOUD · INFRASTRUCTURE AS CODE

Terraform Multi-Cloud Infrastructure

Independent Azure and AWS deployments covering virtual networks, subnets, security rules, Linux VM, EC2, and S3 resources.

AzureAWSTerraform
View repository ↗
ENTERPRISE AUTOMATION / 07
TENANT ATENANT BTENANT C
SHARED CODE · ISOLATED STATE
AZURE · GOVERNANCE · OIDC

Multi-Tenant Deployment Platform

A reusable Terraform platform concept for isolated tenant deployments, remote state, OIDC authentication, monitoring, backup, and controlled release workflows.

TerraformOIDCAzure
Project details ↗
AI-ASSISTED GOVERNANCE / 08
AI ASSIST→PLAN REVIEW→APPROVAL
AI · TERRAFORM MCP · HUMAN REVIEW

AI-Assisted Terraform Governance

Terraform MCP and GitHub Copilot-assisted workflow with reviewed plans, Azure remote state, OIDC, protected environments, and human approval gates.

MCPGitHub CopilotTerraform
View repository ↗
CONTAINERIZATION / 09
DOCKERCOMPOSE
APPLICATION PACKAGING

Dockerized Web Application

Node.js web application packaged with Docker and Docker Compose for repeatable local development and deployment.

DockerNode.jsCompose
Project details ↗
NETWORK SECURITY / 10
◈PRIVATE TUNNEL
LINUX · NETWORKING · SECURITY

WireGuard VPN on Ubuntu

Secure remote-access VPN lab using key authentication, IP forwarding, UFW rules, and controlled routing.

UbuntuWireGuardUFW
Project details ↗
BEHIND THE BUILD

A closer look at the engineering.

Selected project notes explain the problem, design choices, and validation steps. The Kubernetes case study links to the full technical walkthrough. These are personal labs and portfolio builds, not claims of production deployment.

01Azure Landing Zone with TerraformAzure · Terraform · GitHub Actions · OIDC

Problem

Cloud foundations are harder to maintain when networking, compute, diagnostics, and deployment controls are configured inconsistently.

Design

Use reusable Terraform modules for network and compute components, remote state, diagnostics, and a GitHub Actions workflow with federated identity and an approval step.

Validation checklist

  • Run terraform fmt -check and terraform validate.
  • Review the Terraform plan before any apply.
  • Confirm diagnostics and state configuration; document cleanup steps.
View repository ↗
02Automated Terraform Drift DetectionTerraform · GitHub Actions · Azure OIDC

Problem

Manual changes in a cloud portal can leave deployed resources out of sync with the declared Terraform configuration.

Design

Schedule or trigger a workflow that authenticates with OIDC, refreshes state, creates a plan, and reports drift for review instead of silently applying changes.

Validation checklist

  • Make a controlled test change in a disposable environment.
  • Confirm the plan reports the difference.
  • Verify the workflow does not auto-apply and does not store long-lived cloud credentials.
View repository ↗
03Terraform Multi-Cloud InfrastructureTerraform · Azure · AWS

Problem

Learning cloud infrastructure across providers requires understanding both shared IaC patterns and provider-specific resource models.

Design

Keep Azure and AWS deployments independently understandable, using Terraform to define networking and compute resources with provider-specific configuration.

Validation checklist

  • Run format and validation checks for each configuration.
  • Inspect each provider's plan before provisioning.
  • Record outputs and destroy test resources to avoid unnecessary cloud spend.
View repository ↗
04Kubernetes Deployment Strategies in ActionNetflix by Sai · Docker · Kubernetes · Rolling Update · Blue-Green · Canary · Rollback · Recreate
HANDS-ON APPLICATION RELEASE LAB

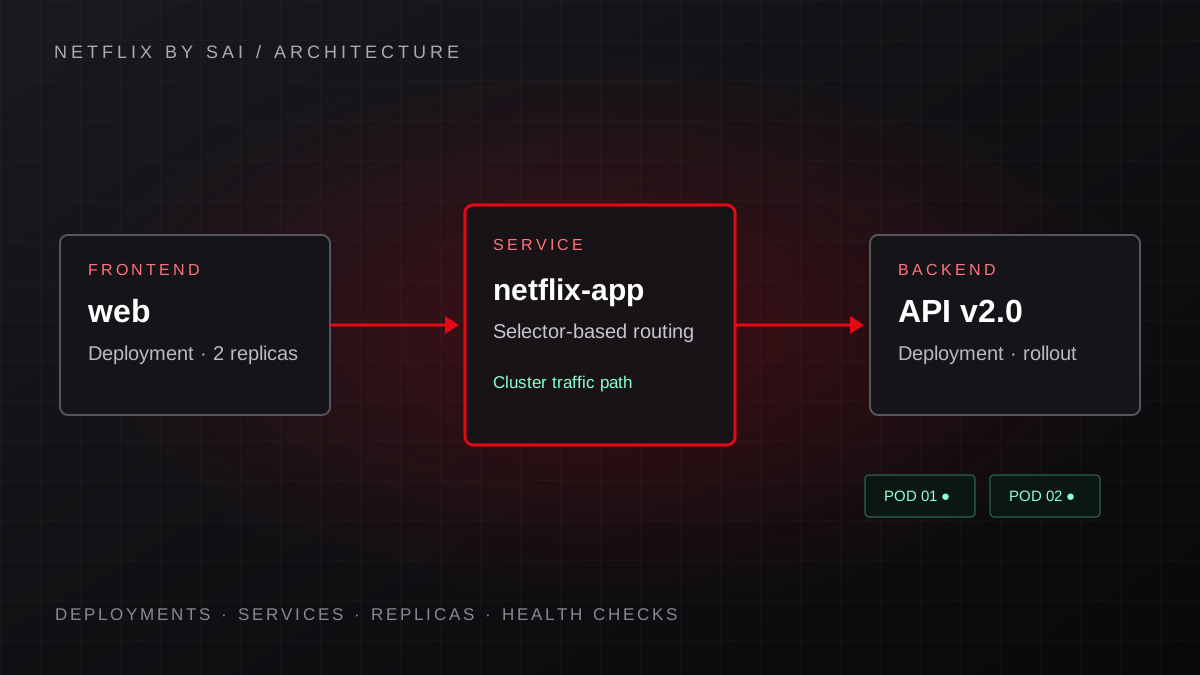
A streaming-style frontend/backend application used to explore Kubernetes releases, version changes, service routing, failure diagnosis, and recovery. The accompanying article documents the implementation and screenshots step by step.

Architecture & workflow

  • Containerize the application components with Docker and validate the application workflow.
  • Deploy frontend and backend workloads into the netflix Kubernetes namespace.
  • Use Deployments and Services to manage replicas and route application traffic.
  • Check the backend health/version endpoint at /api/health after changes.
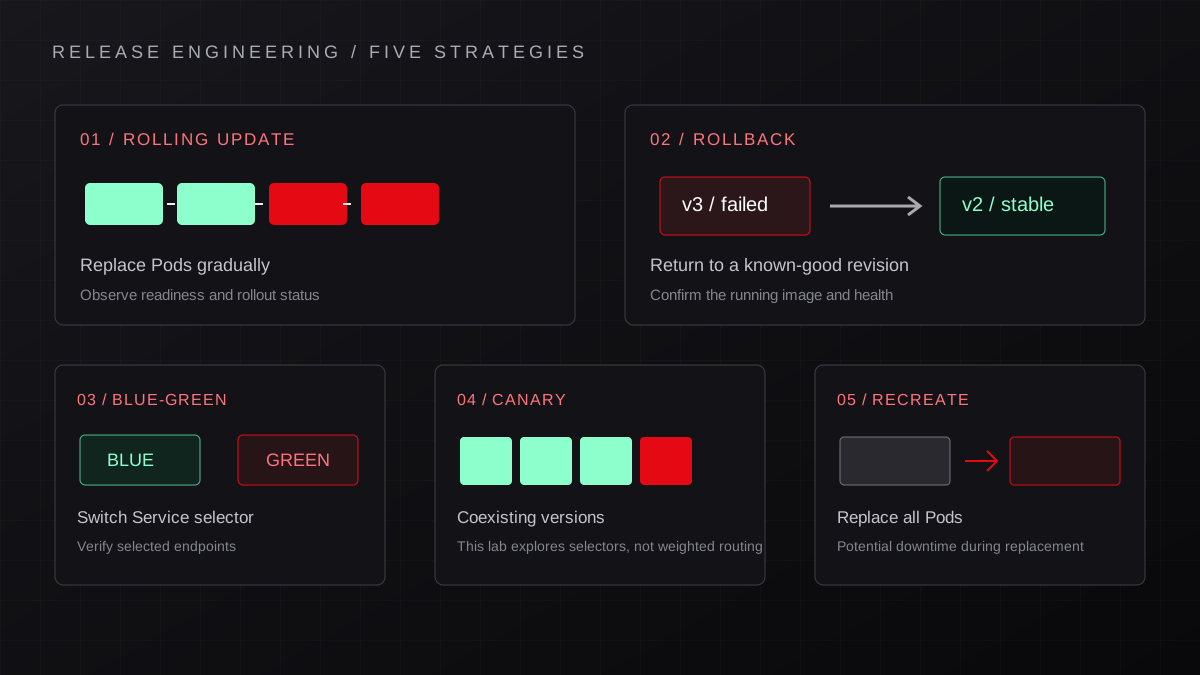
01 / RELEASE

Rolling Update

Move from one application version to another gradually and inspect Deployment and ReplicaSet status.

02 / RECOVERY

Rollback

Recover from a failed rollout by returning to a known-good Deployment revision and validating the running version.

03 / TRAFFIC SWITCH

Blue-Green

Run separate environment versions and examine how a Service selector determines which Pods receive traffic.

04 / COEXISTING VERSIONS

Canary

Explore a limited version rollout and the importance of selectors and endpoint membership. This lab demonstrates selector-based routing, not weighted traffic splitting.

05 / REPLACEMENT

Recreate

Replace existing Pods before starting the new version, highlighting the downtime trade-off of this strategy.

Failure injection & troubleshooting

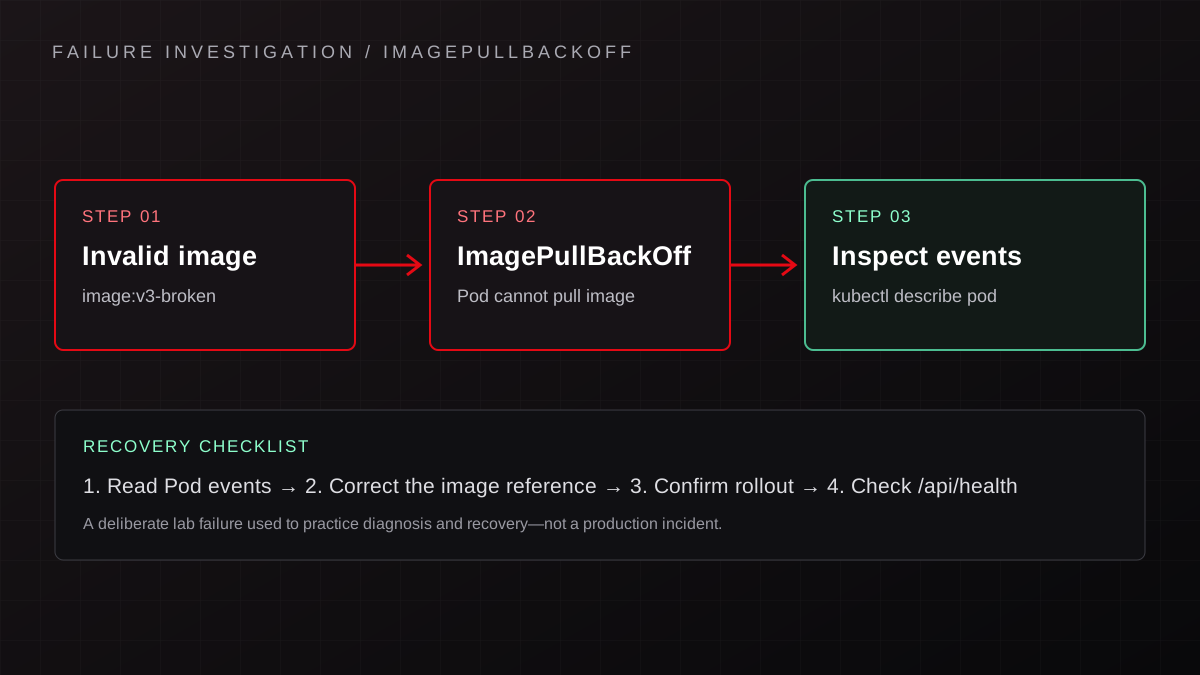
An intentionally invalid image was used in the lab to reproduce an image-pull failure. The investigation used Pod status and events to identify the issue before restoring a valid version.

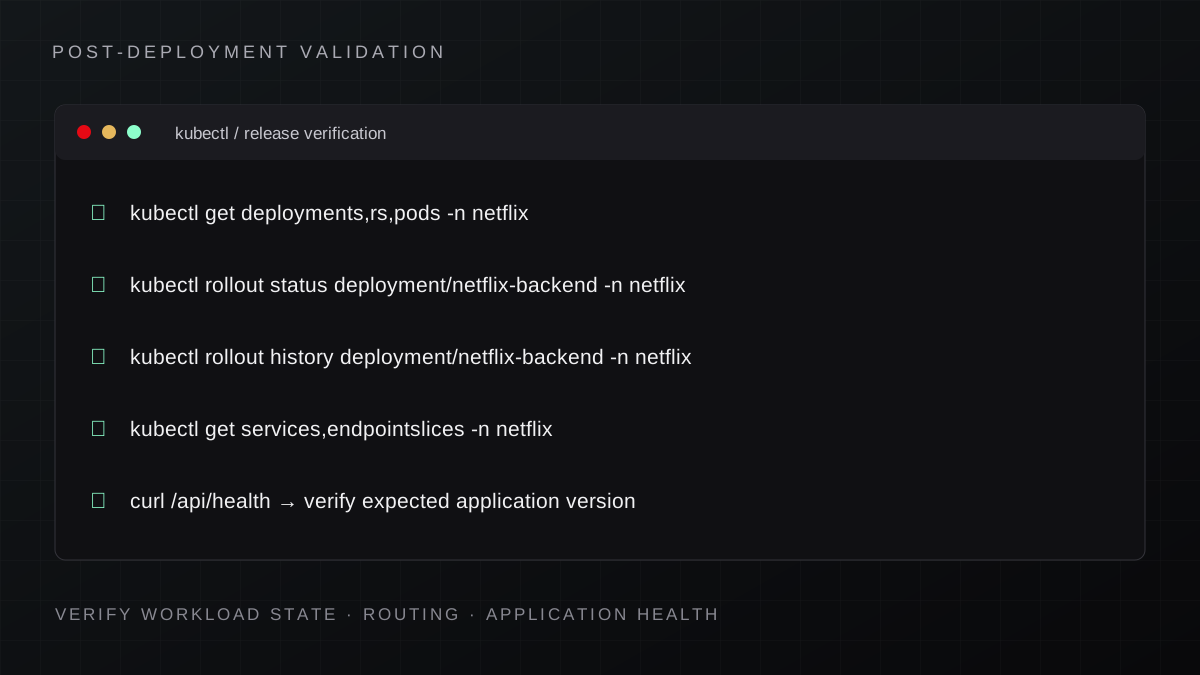
  • kubectl get deployments,rs,pods -n netflix
  • kubectl describe pod <pod-name> -n netflix
  • kubectl rollout status deployment/netflix-backend -n netflix
  • kubectl rollout history deployment/netflix-backend -n netflix

What this project demonstrates

  • How Deployment strategies affect application availability and replacement behavior.
  • How Services and selectors influence traffic routing between versions.
  • How to diagnose ImagePullBackOff through Kubernetes events.
  • Why a successful rollout should be confirmed using workload status and application-level health/version checks.

Project descriptions are a starting point. Link each card to the matching repository and keep claims aligned with what you have actually implemented.

MY TOOLKIT

The stack behind the story.

Technology is the tool. Reliability, clarity, security, and repeatability are the goal.

A

Cloud & Azure

Azure administration · Networking · Identity · Monitoring

↗
⌘

Infrastructure as Code

Terraform · Modules · State · Drift awareness

↗
⇢

CI/CD & DevOps

Azure DevOps · GitHub Actions · YAML · Git

↗
▦

Containers

Docker · Kubernetes fundamentals · Deployments

↗
$_

Systems & Scripting

Linux · Windows Server · PowerShell · Bash

↗
◉

Observability

Logs · Metrics · Troubleshooting · Monitoring concepts

↗
PREVIOUSLY ON MY JOURNEY

Experience that
builds reliability.

My systems background taught me to troubleshoot methodically, document clearly, and think about the operational impact of every change.

JAN 2025 — MAY 2026

Cloud Analyst — HCLTech

Cloud and infrastructure operations, incident troubleshooting, service reliability, and operational support. Detailed responsibilities should align with the resume.

DEC 2023 — DEC 2024

Azure / Windows Administrator

Windows and Wintel administration, server support, incident handling, and infrastructure operations.

CREDENTIALS & CURIOSITY

Learning never rolls back.

Certifications show commitment. Hands-on work shows how I apply the knowledge.

For recruiter verification, compare each credential with its issuer record. View professional profile ↗

THE ENGINEERING JOURNAL

Ideas, documented. Lessons shared.

Notes from building, troubleshooting, and learning across cloud infrastructure, Terraform, Kubernetes, and DevOps.

FIELD NOTE / 01AZURE
LANDING ZONE
↗
AZURE · ARCHITECTURE

Enterprise Azure Landing Zone

Reusable infrastructure, governance, networking, monitoring, and controlled CI/CD workflows.

FIELD NOTE / 02TERRAFORM
MULTI-CLOUD
↗
TERRAFORM · MULTI-CLOUD

Terraform Multi-Cloud Infrastructure

Provisioning patterns across Azure and AWS using Infrastructure as Code.

FIELD NOTE / 03WHY SMART
ENGINEERS DON'T CLICK
↗
AUTOMATION · MINDSET

Part 1 — Why Smart Engineers Don’t Click Anymore

Why repeatable workflows and automation matter more than manual, one-off changes.

FIELD NOTE / 04KUBERNETES
FROM BASICS
↗
KUBERNETES · LEARNING SERIES

Kubernetes From Basics to Advanced — Part 1

Fundamentals that help explain how Kubernetes workloads and core resources fit together.

FIELD NOTE / 07NETFLIX BY SAI
DEPLOYMENT STRATEGIES
↗
KUBERNETES · RELEASE ENGINEERING

Kubernetes Deployment Strategies in Action

A practical walkthrough of Rolling Updates, Rollbacks, Blue-Green, Canary, and Recreate deployments, including failure investigation and recovery.

FIELD NOTE / 05DETECT
INFRA DRIFT
↗
TERRAFORM · GOVERNANCE

Why Infrastructure Changes Without Your Code

A practical look at configuration drift, plan review, and safer infrastructure workflows.

FIELD NOTE / 06ZERO TRUST
ACCESS
↗
AZURE · SECURITY

Building Zero-Trust Access to Private Azure Infrastructure

Identity-driven access, authorization, private networking, and controlled SSH access with HCP Boundary.

MORE NOTES, TUTORIALS & BUILD LOGSBrowse technical blog ↗Visit Hashnode ↗

The site currently links to verified publication listings where an exact article URL has not been confirmed. Replace these with direct article URLs when available.

NEXT UP: SOMETHING GREAT

Have a cloud challenge?
Let's build it better.

I'm interested in Azure Cloud, Cloud Operations, and DevOps opportunities where I can learn, automate, and deliver reliable systems.

SAI KRISHNA / CLOUD & DEVOPSBUILT WITH CURIOSITY, NOT COPY-PASTE.